

Centralized Password Management for Small Businesses: Choosing and Implementing the Right Software

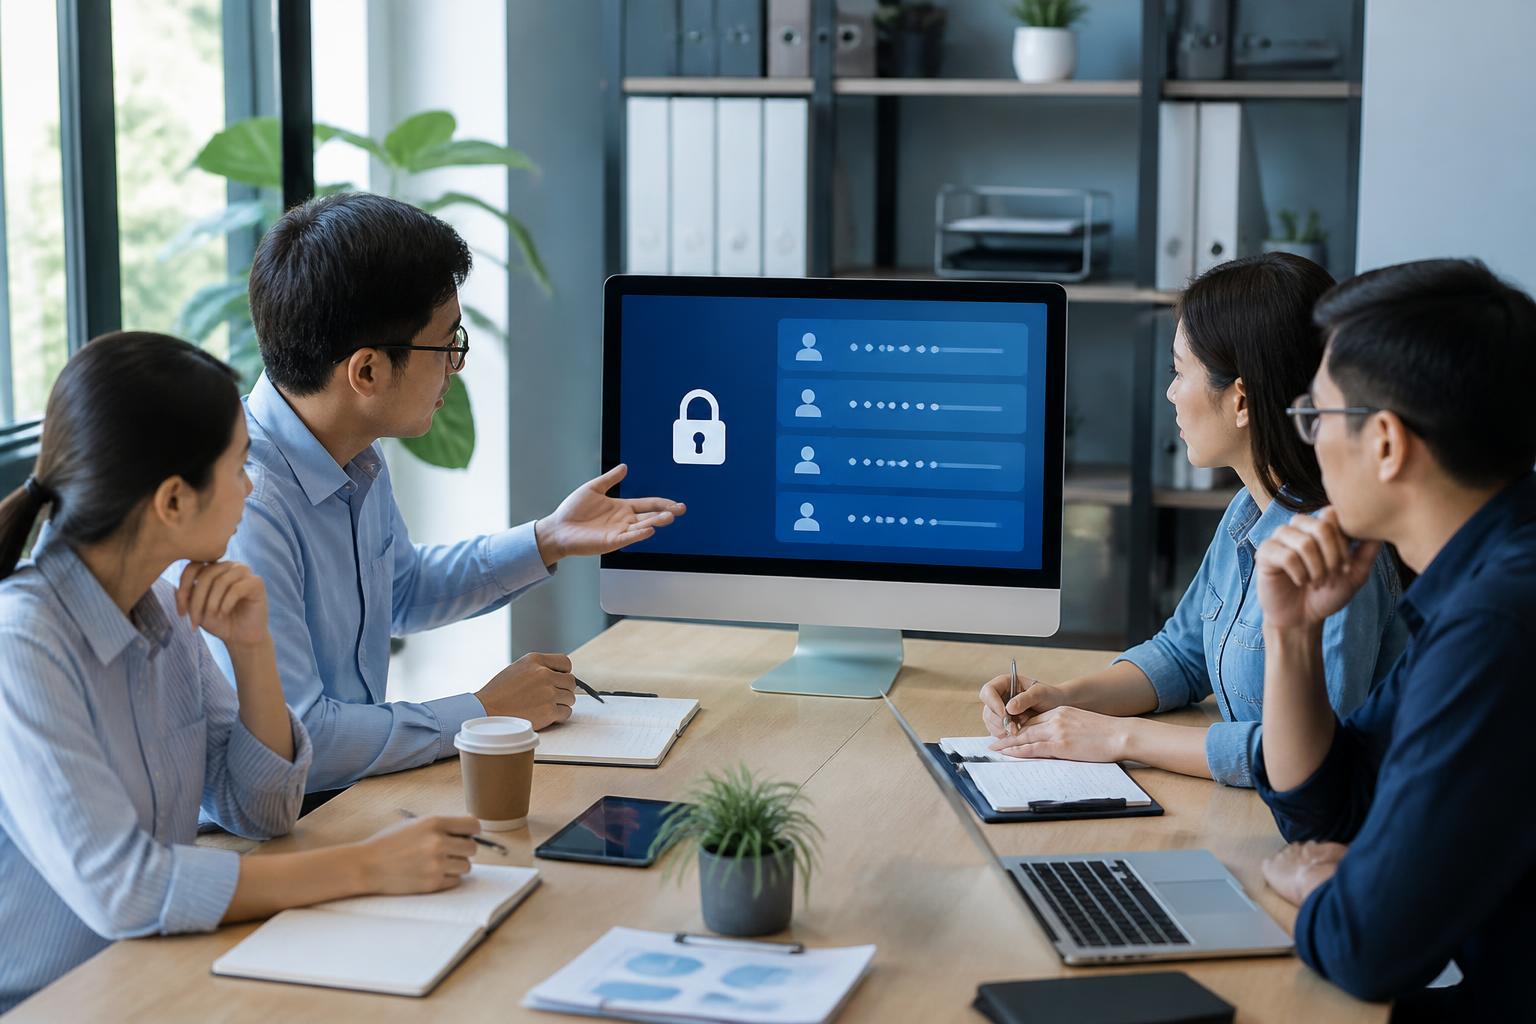
In many small businesses, passwords are still managed in highly manual ways: stored in spreadsheets, sent through chat applications, written in notebooks, or shared through a single account used by the entire team. This approach often begins as a way to save time, but gradually creates more vulnerabilities. When an employee leaves, when access needs to be revoked, or when no one remembers where an account is being used, the business must spend considerable effort checking and changing each service individually.
Centralized password management software is designed to solve this problem. It allows login information to be stored in a protected data vault, permissions to be assigned to individual users, and access to be shared without necessarily exposing the original password. However, installing an application does not automatically mean that the business is more secure. Effectiveness depends on how the software is selected, policies are configured, and usage procedures are maintained in practice.
Why Do Small Businesses Need to Manage Passwords with Software?
Small businesses often have few employees responsible for technology, while the number of online accounts increases very quickly. A team may use email, domains, servers, website administration systems, accounting software, advertising tools, customer service platforms, and many other collaboration services at the same time. Each account has its own permission settings, recovery procedures, and security requirements.
If login information is scattered across many places, the business will have difficulty knowing who has access. Sharing a single password also makes it unclear who is responsible. When an account is exposed, the administrator must not only change the password but also review every place where that password has been used. Centralized management software helps bring accounts into a unified process, thereby reducing dependence on personal memory or habits.
Another important benefit is that the tool supports work handovers. New employees can be granted access according to their roles instead of receiving a list of passwords through messages. When an employee changes departments or leaves the company, access can be revoked from one location. This approach is suitable for businesses that need to control digital assets but do not yet have a dedicated systems administration team.
Features That Should Be Prioritized
Encrypted Storage Protected by a Master Password
Suitable software must protect stored data with a trustworthy encryption mechanism. Users should clearly understand where data is encrypted, who can access it, and under what circumstances the provider can recover the data vault. The master password is the most important layer of protection, so businesses should not use a short, easy-to-guess password or one that is shared with another account.
Businesses should not focus only on encryption claims in advertisements while overlooking how the system operates. They need to read the official documentation on backups, recovery, device management, and what happens if an administrator loses access. A tool with many features but an unclear recovery process can create difficulties when an incident occurs.
Role-Based Access Control
Not every employee needs to see the entire password vault. The person responsible for the website may need access to the content management system and server, but does not necessarily need access to the accounting account. An advertising employee may use a marketing platform account without needing to know the login information for the domain or backup system.
The software should allow businesses to create groups, divide data vaults, and grant access according to job requirements. Businesses should also review granted permissions periodically, because employees’ roles may change. Assigning permissions once and then leaving them unattended for a long period undermines the purpose of access control.
Multi-Factor Authentication
Multi-factor authentication adds a layer of verification beyond the password. When logging in from a new device or performing a sensitive action, users may have to confirm their identity through an authenticator app or a method specified by the business. This feature should be enabled from the early stages, especially for administrator accounts and accounts with permission to share the data vault.
Businesses need to prepare a backup plan before enabling multi-factor authentication for all users. They should determine who is authorized to provide assistance when an employee loses a device, how to change the authentication method, and how to check the list of trusted devices. A good policy must protect accounts while also avoiding situations in which users try to bypass the process.
Password Creation and Assessment
A password generator helps users create a unique string for each service instead of inventing familiar passwords themselves. The more different passwords are across systems, the less an incident involving one service will affect the others. The tool should also warn when login information is duplicated, too old, or used in multiple places.
Automatic warnings should not be treated as absolute conclusions. Administrators still need to consider the importance of each account and establish a processing order. Server administrator accounts, domains, business email, and payment systems generally need to be prioritized over accounts used for secondary tasks.
How to Choose Suitable Software
Before trying a product, a business should create a list of practical requirements rather than choose based on the number of features. It needs to answer basic questions: How many users are there? Is it necessary to share accounts with multiple groups? Do employees use computers or phones more often? Is it necessary to manage server accounts and sensitive technical information? Who will be responsible for administration?
The interface is also an important criterion. If saving, retrieving, and sharing information is too complicated, employees may return to old practices such as sending passwords through messages. Businesses should test the software with a small group, observe which steps cause confusion, and check its usability on commonly used devices. Software that provides strong security but is difficult to use can still fail when deployed widely.
The ability to export and migrate data should also be considered. Businesses should not allow all important information to depend on one service without knowing how to move the data when necessary. They need to read the terms of use, storage policies, and limitations of the service plan carefully. If the tool has a team version, check how users are counted, what administrative permissions are available, and whether access can be revoked when staffing changes.
Costs do not consist solely of subscription fees. Businesses must also account for the time required for setup, training, account inventory, and handling exceptions. A solution that is sufficient and used consistently by everyone is often more valuable than a feature-rich system that does not fit the scale of operations.
A Phased Implementation Process
Inventory Accounts Before Installation
Start by creating a list of the services currently in use. The list should record the service name, person responsible, purpose of use, level of importance, and employee groups that need access. During this stage, the business may discover forgotten accounts, accounts shared by too many people, or services that are still active even though they are no longer needed.
Do not immediately import all old data into the software without checking it. Duplicate information, accounts with unclear origins, and passwords that have been shared too widely should be flagged for processing. Cleaning the initial data makes the password vault easier to manage later.
Set Up Groups and Naming Rules
The data vault should be organized by department, project, or type of service, depending on the business model. Item names should be clear and consistent so users can find the correct account without opening multiple similar entries. The notes section should contain necessary operational information, but it should not become an indiscriminate storage area for unrelated sensitive data.
From the outset, the business should establish who may create new entries, who may change permissions, and when information must be updated. These simple rules help prevent each person from organizing the data vault in a different way.
Test with a Small Group
A test group consisting of an administrator and representatives from different departments will help identify problems before deployment across the company. This group should carry out common scenarios such as logging in on a new device, sharing access with a colleague, changing a password, revoking access, and recovering access after losing a device.
During the testing period, record the steps that users are most likely to perform incorrectly. If employees repeatedly confuse viewing permissions with editing permissions, or do not know how to report an unusual account, the business should adjust its instructions before expanding the rollout.
Train Using Specific Scenarios
Training should not consist solely of introducing buttons and controls. Users need to understand why passwords must not be sent through chat channels, why each person should have an individual account, and what to do when they suspect that login information has been exposed. Scenarios closely related to daily work are easier to remember than general rules.
The business also needs to designate a support contact. When they encounter an error, employees must know whom to contact instead of creating a new sharing method on their own. Administrators should prepare brief instructions for common operations and update them whenever the process changes.
Common Mistakes
The first mistake is simply putting old passwords into the vault without changing information that has previously been widely shared. Centralized storage cannot automatically make an exposed password safe. After completing the inventory, the business should change important passwords and ensure that each service uses separate credentials.
The second mistake is giving too many people administrative privileges. High-level permissions should be granted to an appropriate number of people for backup purposes, and there must be a plan for periodic review. Administrator accounts should not be used for routine work if the software allows roles to be separated.
The third mistake is forgetting to plan for employees leaving the business. The offboarding process should include revoking access in the password management software, changing shared accounts, and checking the services that the person previously managed. This work requires coordination among management, human resources, and the person responsible for technology.
The final mistake is treating the software as a one-time installation solution. New accounts will continue to be created, employees will change, and access rights may arise from projects. The business should set aside regular times to review users, permission groups, devices, unused accounts, and security alerts.
Make the Software Part of the Operating Process
Effective password management does not depend entirely on a particular product. The greatest value lies in the business knowing which accounts it has, who is responsible for them, and why access was granted. The software is simply a tool that makes this process clearer, more consistent, and easier to review.
Small businesses can start with their most important accounts, deploy the software to a limited group, and then gradually expand. This approach helps reduce work disruptions, gives users time to become familiar with the system, and allows policies to be adjusted based on actual experience. When every member understands that protecting passwords is part of the job rather than an extra formality, the system can deliver lasting value.