

Enterprise Password Management Software: Building a Layer of Defense from Login Habits

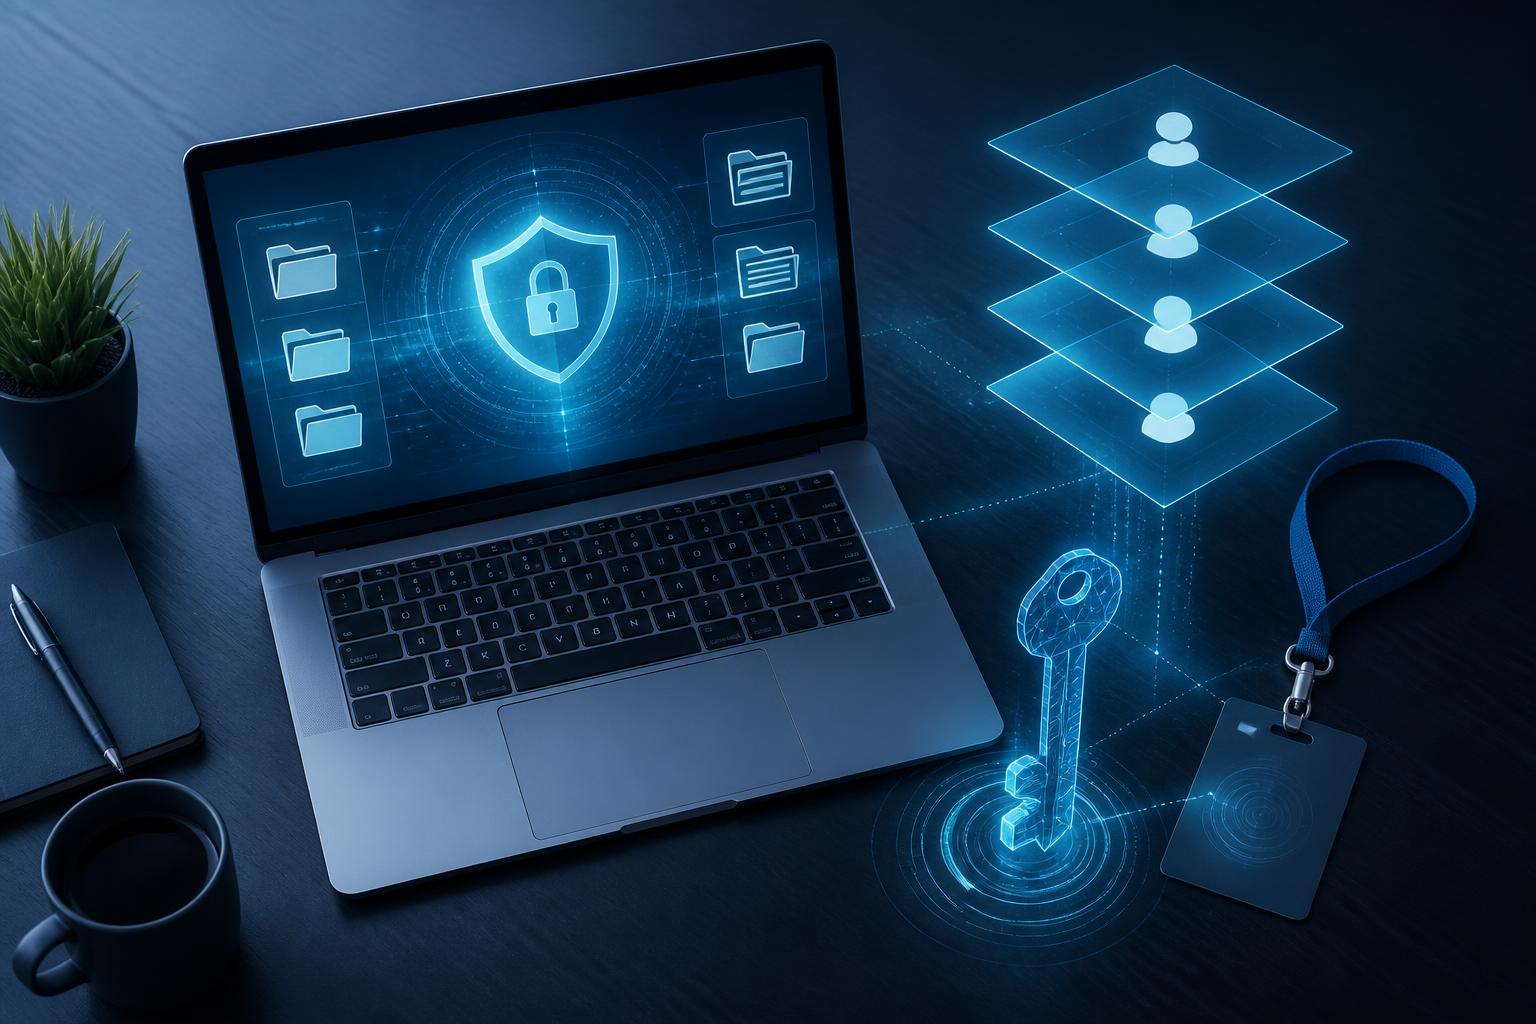
In many businesses, passwords are still treated as a minor detail in operational processes. Employees write login information in spreadsheet files, save it in browsers, send it through chat applications, or use a shared account for the entire team. These practices often arise from immediate convenience, but the more online services are used, the harder the risks become to control. When someone leaves the company, changes positions, or loses a device, the business may not know exactly which accounts have been affected.
Enterprise password management software is designed to address this problem at the system level. The tool not only stores passwords in a secure vault, but also supports access permissions, controlled sharing, creation of new credentials, activity monitoring, and access revocation when necessary. The value of the software lies in turning password management from a personal habit into a process that can be controlled, handed over, and audited.
Why does manual management quickly become unsafe?
A small business may start with a few email accounts, a website administration system, and accounting software. However, this list often grows over time. Each department begins using additional advertising platforms, customer-care software, file storage services, design tools, or collaboration applications. Without a centralized place to manage them, login information becomes scattered across many different channels.
The first risk is password reuse. Users tend to choose a few easy-to-remember strings for multiple services, especially when they have to log in frequently. If the credentials for just one service are exposed, other accounts using the same password may also be threatened. The second risk is opaque account sharing. A password sent in a chat group may continue to exist on multiple devices and in backups, even after the message is no longer visible in the ordinary interface.
The third risk concerns the employee lifecycle. When an employee leaves the company, manually changing all passwords is often time-consuming and easy to overlook. If several people use the same account, the business also finds it difficult to determine who made a particular change. Password management software does not eliminate every risk, but it helps organizations reduce their dependence on memory, spreadsheets, and uncontrolled communication channels.
Core functions of password management software
Encrypted password vault
The central function of the software is a repository for storing credentials. Each user can manage personal data, while shared accounts are placed in a team or department vault. Data needs to be protected both during transmission and while stored. Businesses should also clearly understand how the provider handles encryption keys, recovery mechanisms, and data protection when a device is lost.
Some solutions use a model in which the provider cannot directly read the contents of a customer’s vault. However, the name or claims regarding a security architecture should not be the sole basis for a choice. Businesses need to review technical documentation, data policies, recovery plans, and how the product responds when a user loses their unlocking information.
Strong password generation and organized changes
A password generator helps users create long, hard-to-guess strings that are different for each service. When a new account is created, employees do not need to come up with an easy-to-remember password or reuse old information. Depending on the capabilities of each product, the software may also help detect duplicate, overly weak, or long-unchanged entries.
However, changing passwords on a fixed schedule is not always the only solution. If password changes occur too frequently without being accompanied by multifactor authentication and access controls, users may create predictable variations or record passwords in unsafe places. Policies should be based on the sensitivity of the account, the status of any breach, personnel changes, and the requirements of each service.
Sharing access rights instead of sharing passwords
This is an important difference between a personal password vault and a solution designed for businesses. Administrators can grant members permission to use an account without necessarily allowing them to see all of the confidential information. When an employee moves to another department, access can be revoked from the group instead of having to locate and change every related password.
The permissions model should be sufficiently detailed to match actual circumstances. Customer support employees may need access to customer-care tools but not to the payment system. The content team may use a website administration account within a limited scope, while the highest administrative privileges are reserved for a few designated people. Role-based permissions help reduce both the risk of misuse and accidental actions caused by overly broad access.
Activity logs and auditability
For important accounts, businesses need to know who has been granted access, who has used the login information, and whether that access is still valid. Activity logs do not replace a specialized security monitoring system, but they provide a useful layer of information for review. When an incident occurs, this data helps narrow down changes, identify the affected group, and support the process of revoking access.
Logs are also valuable in day-to-day operations. Administrators can detect that a former employee’s account is still in a group, that a department’s access has changed but has not been updated, or that sensitive login information is being shared more widely than necessary.
Criteria for choosing a solution suitable for the business
No single password management software is suitable for every organization. Businesses should begin by listing the types of accounts that need protection, the number of users, the groups with different permissions, and the handover requirements when personnel change. This helps avoid choosing based on the number of features without addressing the actual operational problem.
User management capabilities are an important criterion. The product should support group creation, role-based permissions, rapid access revocation, and data transfer when a member leaves the organization. If the business has a centralized identity management process, the ability to connect with the existing login system may help reduce separate accounts and simplify administration.
The user experience should also be taken seriously. A tool with many layers of protection but overly difficult operation may cause employees to find workarounds, save passwords elsewhere, or share them outside the established process. Applications for commonly used devices, browser extensions, autofill functions, and a reasonable recovery process can directly affect the level of user adoption.
Businesses should also assess the provider’s transparency. Questions to ask include where the data is stored, how backups are protected, how the provider assists when an administrator account encounters a problem, whether users can export their data, and how data deletion is handled when the service ends. These are no less important than the interface or subscription price.
How to implement it so employees actually use it
Implementing password management software should not begin by moving all the disorganized data into a new vault. First, the business should create an inventory of important accounts, identify their owners, classify their sensitivity, and remove accounts that are no longer used. Duplicate or unclear entries should be verified before being added to the system.
The pilot phase can begin with a small group consisting of the information technology department and a business team that frequently shares accounts. The goal is not only to check whether the software works, but also to assess the processes for granting permissions, approving access, handing over responsibilities, and responding when someone loses a device. Obstacles during this phase often indicate that internal policies need to be clarified further.
After the pilot, the business should issue principles that are concise and easy to follow. Employees need to know which types of accounts must be stored in the vault, when access may be shared, who has approval authority, and what to do when they suspect information has been exposed. Training should focus on real-world situations rather than merely introducing features. A simple process, reiterated at the right time, is often more effective than a long document that few people read.
The transition should also include a plan for changing passwords according to priority. System administrator accounts, executive email accounts, data storage services, and platforms related to payments should be handled first. The business can then expand to other operational accounts. Each change should be recorded to avoid situations in which the passwords in the vault no longer match the actual systems.
Software does not replace an entire security strategy
Password management is an important layer of defense, but it is not the only solution. Businesses still need to enable multifactor authentication for supported services, limit administrative privileges, update software, and teach employees to recognize phishing. If a user’s device access is compromised or the user is tricked into providing an authentication code, the password vault alone cannot handle all the consequences.
Information for recovering an administrator account needs to be prepared carefully. The business should identify the responsible person, establish a communication method for situations in which the primary administrator cannot access the account, and determine how emergency access will be checked periodically. Backup documentation must be protected to the same standard as the primary data, while an uncontrolled copy should not be created in a text file or on paper and left just anywhere.
Finally, the software’s effectiveness should be evaluated through behavior and processes, not merely by whether the application has been installed. Businesses can periodically review unused accounts, the permissions of personnel whose roles have changed, reused passwords, and groups with overly broad access. When these activities become part of regular governance, password management software can fulfill its role as an access-control platform rather than merely a place to store login information.