

Team Password Management Software: A Risk-Reduction Platform for Digital Operations

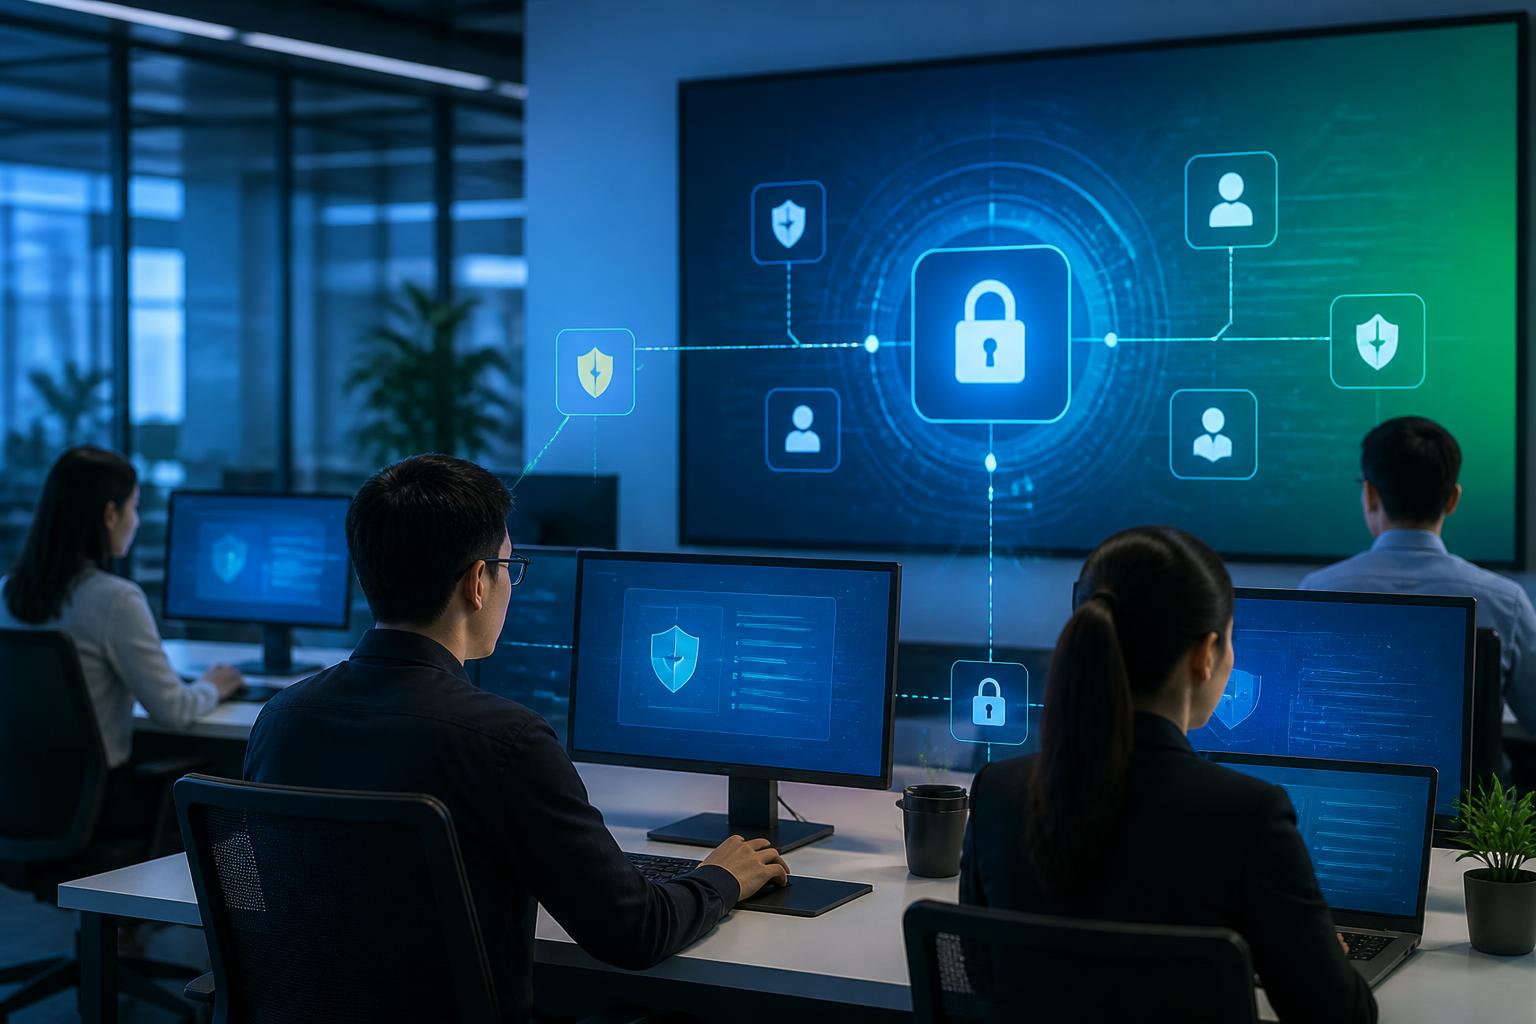
In many businesses, passwords are still handled as pieces of information that can be quickly sent by email, messaging apps, or shared spreadsheets. This approach often starts from a very practical need: an employee needs access to an advertising account, website administration system, support inbox, or server; the person in charge only needs to send the login details so work can continue without interruption. However, as the number of accounts increases and more people join the team, manual sharing quickly becomes a weakness in operations.
Team password management software is designed to address this problem. The tool not only stores passwords in an encrypted vault, but also supports access control, activity logging, secure credential generation, and access revocation when personnel changes. The main value of the software lies in transforming a process that is often overlooked into one that can be controlled, reviewed, and improved over time.
Why does manually storing passwords create risks so easily?
A single account may be used by several different departments. Marketing employees need access to advertising platforms, the content team needs to enter the website administration system, customer service staff need to use a shared inbox, while technicians need administrative access to servers or storage services. If everyone stores information in their own way, the business will quickly lose the ability to know where passwords are stored, who is using them, and which access permissions are still active.
Spreadsheets are a common example. They can help consolidate information at the beginning, but they often lack the layers of protection and control mechanisms appropriate for sensitive data. A file stored on a personal computer, attached to an email, or shared through a common folder may continue to exist even after the user is no longer working on the project. Password changes also become difficult to track because not everyone updates the latest version in the correct location.
Sending passwords through chat applications creates similar problems. The content may be stored in the conversation history, forwarded to someone who does not need access, or remain on a device that is no longer under control. When an employee leaves, the business cannot be certain that all information has been deleted from personal channels. The risk does not necessarily come from a sophisticated attack; sometimes, a loosely managed handover process is enough to create a security gap.
How does team password management software work?
Basically, the software creates a centralized vault for login credentials and related sensitive data. This vault is protected by each member’s individual account, along with additional authentication mechanisms depending on the product. Users can access the accounts for which they have permission without necessarily seeing the original password. This is an important difference from directly sending login details to each person.
Administrators can organize data by team, project, or service type. For example, website accounts can be separated from advertising accounts, server information can be placed in a separate group, and internal accounts can be restricted to the human resources department. This classification helps limit the scope of access and reduces the likelihood that an employee will see more information than their job requires.
A suitable system will generally provide activity logs so the business can know which accounts were accessed, when permissions changed, and who performed administrative actions. Logs do not replace proactive monitoring, but they make post-incident investigations clearer. When an account shows signs of unusual activity, administrators can determine the scope of the impact and take action instead of having to ask every team member individually.
Features to evaluate before making a choice
Permissions based on roles and actual needs
Access control is a core feature of password management software for teams. Businesses should check whether the tool allows them to create groups and limit viewing, usage, or editing permissions. An employee who only needs to log in to a service to perform their work does not necessarily need permission to change the password or share that information with others.
The access-control mechanism must also accommodate constantly changing situations. Personnel may participate in multiple projects, transfer departments, or provide support for only a short period. If granting and revoking permissions is too complicated, administrators may delay necessary actions. A clear interface that allows them to quickly see which members have access to each data vault will help reduce operational errors.
Multi-factor authentication and integration capabilities
The master password for the management account is only one layer of protection. The platform should support multi-factor authentication to reduce the risk of an account being taken over when login information is exposed. Businesses should also consider the ability to integrate with the identity systems they already use. When personnel log in with corporate accounts and permissions are synchronized with the employee directory, granting or terminating access becomes more convenient than managing everything manually.
Depending on the organization’s size, technical teams may be interested in the ability to integrate with automated processes, support tools, or human resources management systems. However, integration should not be treated as the sole criterion. Software with many connections but complicated configuration, difficult auditing, or poor alignment with internal operational capabilities can create an additional burden instead of reducing workload.
Secure sharing without exposing the original password
In practice, the need to share accounts will continue to exist. The issue is how the business shares them. The tool should allow access to be granted directly from the vault while limiting the copying of sensitive information when the work process does not require it. For some accounts, a business may need to provide temporary access to contractors or vendors. In that case, access duration and the ability to revoke access quickly are factors that deserve priority.
It is also necessary to distinguish between accounts with shared passwords and accounts with separate permission mechanisms for each member. If a service supports individual accounts, the business should prioritize that model because it is easier to trace and revoke access. Password management software cannot fully compensate for a weak access-control model in the underlying service itself.
Logs, alerts, and auditability
Not every business needs a complex alerting system, but every team needs to know when important data is changed. Check the ability to track edit history, sharing history, and unusual login attempts. Reports should be easy enough to understand that the person responsible does not have to rely entirely on technicians every time they want to review access permissions.
Auditability is also related to the ability to export data and retain information when changing platforms. Businesses should carefully review the provider’s policies regarding data ownership, backup, recovery, and service termination. A good security tool should not turn customer data into a locked vault that the business cannot manage when it needs to switch platforms.
Deploying the software without disrupting work
Effective deployment should begin by creating an inventory of accounts and classifying their importance. Website administration, server, email, advertising, and storage service accounts should be reviewed first. The business needs to identify the business owner, users with administrative rights, the groups currently using the accounts, and the status of recent password changes. This stage often reveals accounts that have been forgotten or are still tied to the personal email addresses of former employees.
Once the inventory is complete, the business should design a simple vault structure. It can be organized by department, project, or sensitivity level, but too many small groups should be avoided because they make information difficult for users to find. Each group should have someone responsible for reviewing its members and access permissions. A clear structure from the beginning will make future expansion less problematic.
The next step is a pilot with a small group. This group may include representatives from technical, marketing, and operations management teams to test different situations. They should try creating accounts, sharing access, revoking access, changing passwords, and handling cases in which a member is no longer involved in a project. Feedback from the pilot will help identify overly complicated steps before the software is deployed across the entire company.
User training is no less important than installing the tool. Employees need to understand that the software is not a place to store every type of data indiscriminately. They need to know when to use a shared vault, when to create personal credentials, how to report suspicions, and why accounts must not be shared outside established procedures. The shorter and easier the rules are to apply, the higher the likelihood of compliance.
Managing the password lifecycle after deployment
The software will only be effective if the business has a regular review process. Important accounts need to have their owners, authorized members, and recovery methods checked. When an employee changes positions or leaves the company, revoking their access in the software must be included in the mandatory handover checklist, along with disabling their account on the underlying service when necessary.
The business should also establish rules for situations in which passwords need to be changed. Not all accounts have the same level of risk, so the frequency and method of handling changes can be based on the role of each service. A system administrator account requires a stricter process than an account used for a less sensitive tool. Most importantly, the business must know which accounts should be prioritized and who is responsible for taking action.
When there is suspicion that information has been exposed, the response process should clearly define the steps: lock or change the password, revoke login sessions, review logs, assess related accounts, and record the cause. Having a process in place enables the team to act more quickly and avoids prolonged debate over who has the authority to respond. The software helps provide data, but decisions and responsibility still belong to the business.
Limitations that should not be overlooked
Password management software is not the only solution for information security. If a user’s device is infected with malware, a corporate email account is compromised, or a user is tricked into providing an authentication code, the password vault may still be affected. Therefore, the tool needs to be combined with software updates, device protection, multi-factor authentication, phishing-awareness training, and least-privilege access control.
Businesses should also not assume that every product with an attractive interface is suitable. They need to consider the encryption model, how the provider handles data, account recovery options, storage location requirements under internal policies, and the quality of support. This information should be compared with the business’s security policies and legal requirements rather than evaluated solely on the basis of a feature list.
Finally, the tool will not solve the problem if the team continues to create shared accounts outside the system, record passwords in personal notes, or grant broader access than the work requires. The value of the software emerges when it becomes a natural part of everyday operational processes.
Conclusion
Team password management software helps businesses move from arbitrary credential sharing to a model with clear access controls, logs, and responsibilities. The benefits lie not only in more secure storage, but also in the ability to control the account lifecycle as projects, personnel, and vendors change.
To make the right choice, a business should start with the size of its team, the types of accounts it manages, and the common risks in its current processes. A suitable tool needs to be easy for employees to use, sufficiently robust for administrators, and capable of evolving with operational needs. When deployed alongside clear policies and sound security habits, the software can become a significant supporting foundation for more sustainable digital operations.