

Website Administration Permissions: Reducing Risks from Overlooked Accounts

Many websites receive careful investment in their interface, content, and performance, yet the management of administrative accounts is often overlooked. During operation, an account may be created temporarily to handle a task, shared among multiple people, or left with high-level permissions even after its responsibilities have changed. These habits create security gaps that website owners often notice only after an incident occurs.
Managing website administration permissions is not simply a matter of creating a few additional accounts with different passwords. It involves determining who can access the system, what actions they can perform, within what scope, and for how long. When permissions are designed appropriately, a website can continue to operate flexibly without granting overly broad access to every team member.
Why Should Access Permissions Be Controlled?
Every login account is a point that can affect a website. Depending on the system, a person with high-level permissions may be able to change content, install extensions, modify configurations, create new accounts, or access data unrelated to their daily work. If that account’s login information is exposed, used incorrectly, or left active after the user is no longer responsible for the work, the consequences can extend far beyond a single post or page.
Risks also arise when multiple people share one account. In this situation, it becomes difficult to determine who performed a specific action. When content is deleted, configurations are changed, or a new account is created for no clear reason, the operations team lacks a basis for investigation. Shared accounts also make it inconvenient to revoke access, because changing the password may affect many people who are still working.
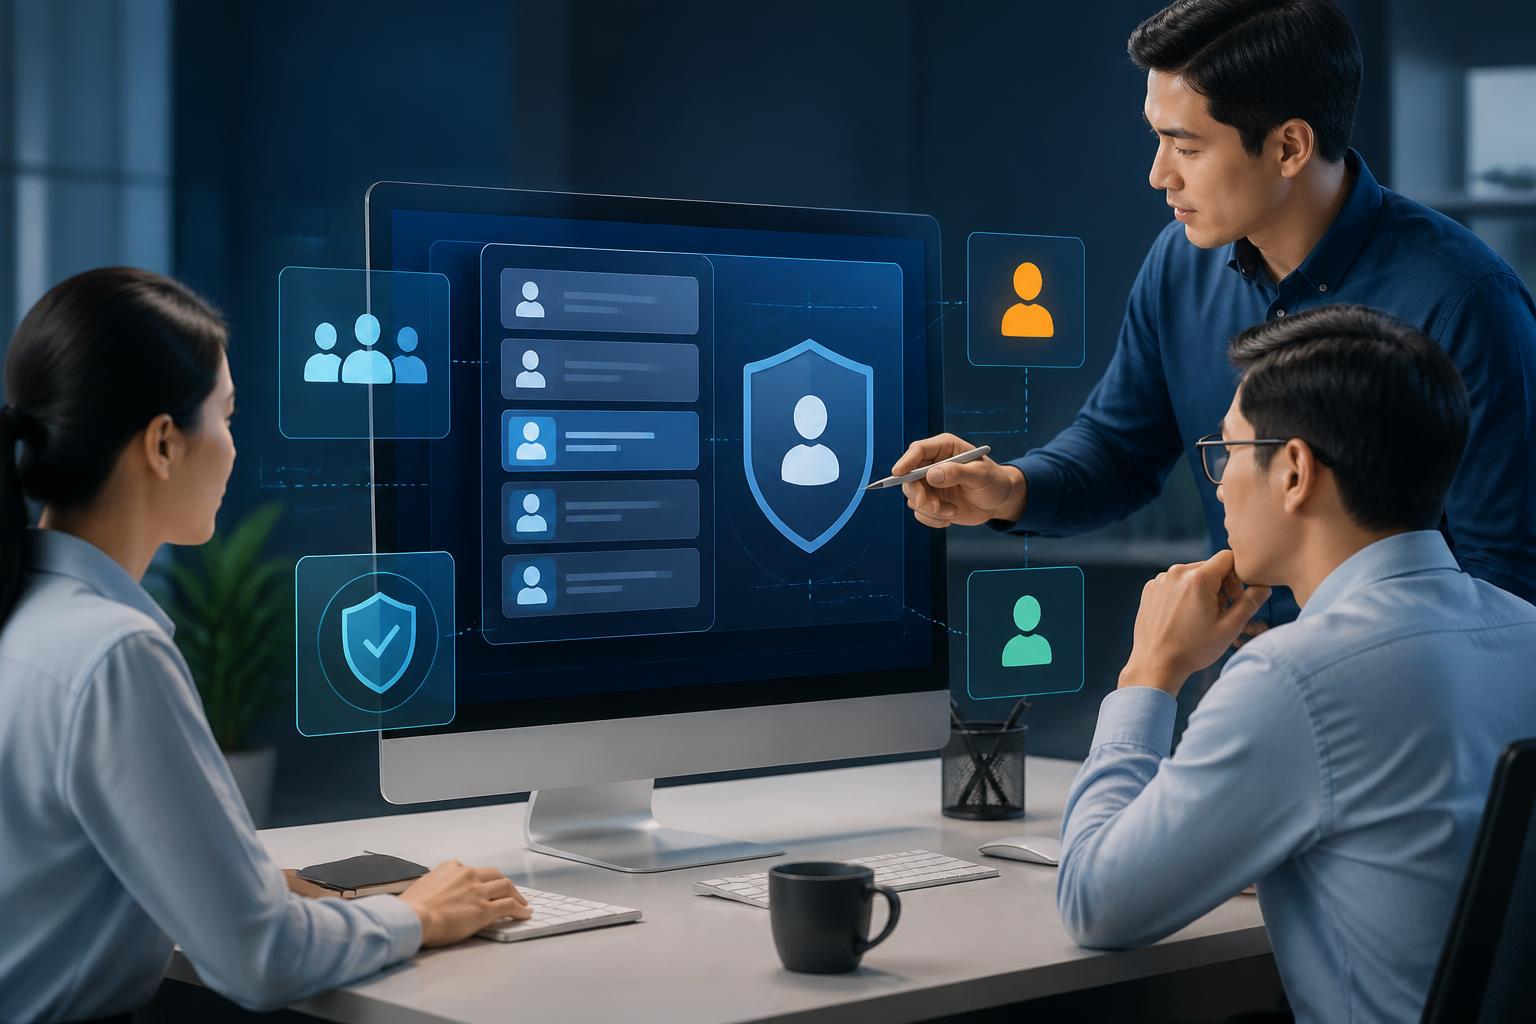
Good access management helps separate responsibilities and establish clear procedures. A writer needs only drafting permissions, an approver can review and publish, while only the person responsible for technical matters needs configuration-related permissions. This separation does not eliminate risk entirely, but it reduces the number of sensitive actions each account can perform.
Start by Creating an Account Inventory
Before changing permissions, it is necessary to know which accounts currently exist on the website. The list should include administrator accounts, editorial accounts, service-provider accounts, technical-support accounts, and connections that can access the server or related tools. Do not check only the content management area and conclude that all access has been controlled.
For each account, record the person or department using it, the purpose of access, the scope of its work, the creation date, and its current status. If the owner or reason for an account’s existence cannot be identified, that is a sign that it needs to be reviewed. An account that is no longer being used should not retain its permissions simply because it has not yet caused a problem.
An inventory should be conducted regularly and after important changes such as an employee leaving, a change in the responsible organization, a server migration, or the deployment of a new tool. This is an ongoing management task, not something to be handled once and then forgotten.
Design Permissions Around Actual Responsibilities
An important principle is that each person should have only the permissions necessary to complete their assigned work. If a team member only updates articles, there is no clear reason for that account to be able to install extensions or change system configurations. Similarly, someone responsible for images and content does not necessarily need access to technical data or the account-management area.
Assigning permissions according to responsibilities helps limit the impact of operational errors. Someone may accidentally delete content or change a setting, but the scope of the damage will be narrower if the account does not have system-wide permissions. This approach also makes it easier to train new team members, because each account has a specific purpose instead of a difficult-to-explain set of permissions.
In many content management systems, permissions are divided into roles with different levels of access. The names may vary between platforms, but the underlying approach is similar: distinguish between people who create content, edit it, approve it, and administer the technical system. Do not choose the highest-privilege role simply because it is the default or the most convenient option at the beginning.
Limit the Highest-Level Administrative Permissions
The highest-level administrative permissions should be reserved for a very limited number of people who are genuinely responsible for the system. This account can change many important components, so it should be used carefully and not for everyday editorial work. When someone regularly posts using an account with maximum privileges, both the risk of operational mistakes and the risk of account compromise can have broader consequences.
A sensible approach is to create separate accounts for different tasks. A technical administrator can use an administrative account when configuration changes are needed, then use a lower-privilege account for routine activities. This also makes it easier to review the action history, because the account name accurately reflects the person performing the action instead of all activities appearing under one shared name.
Do Not Overlook Third-Party Accounts
A website may involve multiple external parties, such as developers, server-management providers, marketing services, or project-based collaborators. During the period of work, granting third parties access may be necessary. However, that access should be tied to a specific scope and duration rather than left in place indefinitely after the work has ended.
Before granting access, the website owner should determine which areas the external party needs to access and what actions they need to perform. If they only need to review content, they should not be given permission to change configurations. If they need to resolve a technical issue, access can be enabled for the duration of the work and revoked once it is complete. All important changes should be documented so that the relevant people know which accounts currently have access and why.
Revoking access should not be understood as a lack of trust in a partner. It is a normal part of the operating process, similar to deactivating an access card when a project ends. Temporary access without a review date can easily become permanent access.
A Strong Password Is Only One Layer of Protection
Using a separate password for each account is a fundamental requirement. Reusing the same password for the website, email, and other services increases the scope of the impact if information is exposed in one place. Login information should be stored securely, rather than being sent casually through unsuitable channels or written somewhere that many people can view.
If the system supports multi-factor authentication, it should be enabled for important accounts, especially those with administrative permissions. This is not a reason to disregard access control. An account can still be misused by its owner or compromised if additional authentication information is not protected. Multi-factor authentication and properly assigned permissions address two different issues, so they should be combined rather than using one measure as a replacement for the other.
When someone changes devices, loses access to an authentication method, or leaves the organization, the relevant information should also be updated immediately. Account-recovery methods should belong to a clearly responsible person and should not be tied to the personal email address of an employee who has left the project.
Review Permissions After Every Organizational Change
Access permissions often become disorganized not because of one wrong decision, but because many small changes accumulate over time. An employee may move from writing content to management, a collaborator may take on additional responsibilities, a new organization may assume technical duties, or a project may end. Any of these events can make existing permissions inappropriate.
Therefore, every change in personnel or procedures should be accompanied by a permissions review. A regular review schedule can be established to confirm which accounts are active, which roles need adjustment, and which permissions need to be revoked. This does not need to become a complicated procedure. Having someone responsible, a clear checklist, and consistent handling principles already creates a substantial foundation.
The review should cover accounts that are no longer in use, accounts with unusually high permissions, shared accounts, external partners’ access, and account-recovery methods. If the website has activity logs, this data can help identify permissions that are rarely used but remain active, as well as actions that require further review.
Balance Security and Work Efficiency
Overly broad permissions create risks, but excessively restrictive permissions without supporting procedures can also bring work to a standstill. When team members must constantly wait for one particular person to perform routine actions, they may be inclined to share accounts or request temporary access without properly documenting it. Therefore, the goal is not to lock everything down, but to create appropriate permissions and transparent alternative procedures.
Sensitive actions may require approval or a second review. For daily work, an account should have enough permissions to complete its tasks without constant intervention. If a role frequently requires requests for additional access, that is a sign that the permission design does not accurately reflect the actual work and needs to be adjusted in a controlled manner.
Internal guidelines also play an important role. Team members should know what their accounts are intended for, must not share login information, should know whom to notify when they detect something unusual, and should understand what to do when their responsibilities end. Clear procedures help turn security from a technical requirement into an operating habit for the entire team.
Conclusion
Managing access permissions is an essential part of protecting a website, even though it is usually not visible on the public interface. Starting with an account inventory, assigning permissions according to responsibilities, limiting the highest-level administrative accounts, controlling third-party access, and conducting reviews after every change will make the system easier to manage.
There is no single access-control model suitable for every website. The size of the team, the type of data, the platform in use, and the operating model will determine the level of detail required. Nevertheless, the core principle remains consistent: every account needs a clear owner, a specific purpose, and only sufficient permissions. When this principle is maintained consistently, the website will have fewer unnecessary access points and a more secure foundation for long-term development.