

Multi-Factor Authentication for Websites: A Practical Line of Defense Against the Loss of Administrative Control

Website administrator accounts typically have the broadest access to content, configurations, user data, and related services. When protected only by a password, such an account can become a weak link even if the server, source code, and backup systems have been carefully secured. A password exposed through a fake login page, reused across multiple services, or guessed because it is too simple can all pave the way for unauthorized access.
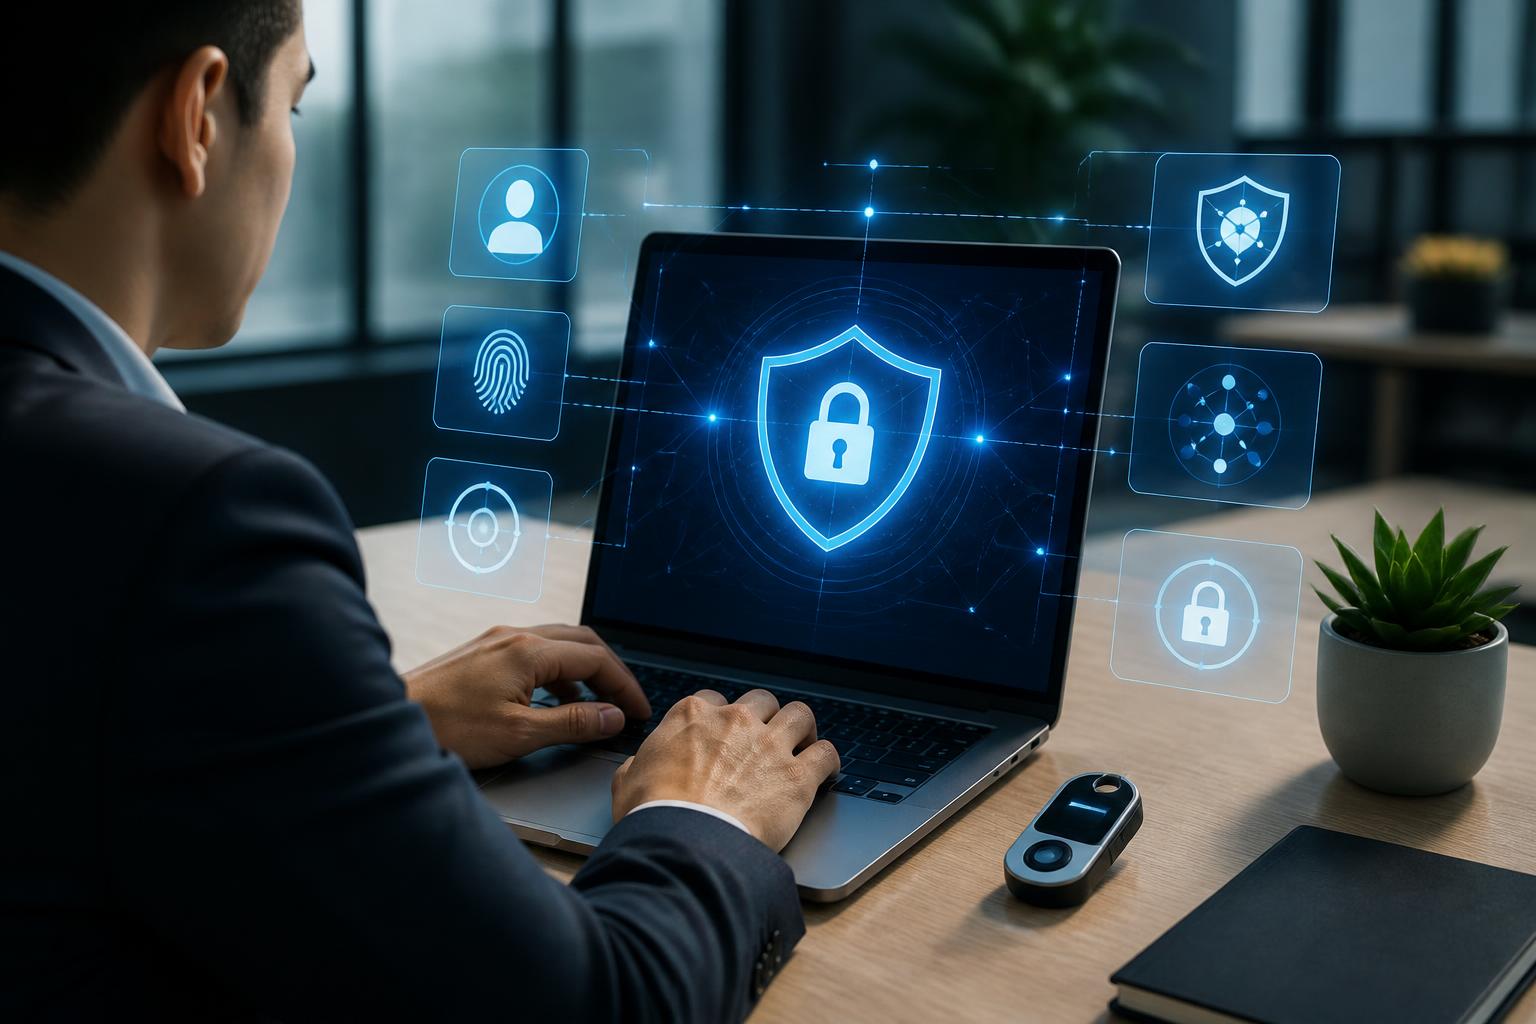
Multi-factor authentication, commonly known as MFA, adds another identity check beyond the password. Users may be required to confirm their identity through an authenticator app, security key, notification on a trusted device, or another suitable method. This mechanism does not make a website immune to every attack, but it creates an important additional barrier when a password has been exposed. For MFA to be effective, website owners need to treat it as a complete management process rather than simply enabling an option in the settings.
Why are passwords no longer a strong enough layer of protection?
Passwords have many limitations even when users are advised to create long and difficult-to-guess passwords. People tend to rely on familiar patterns to make passwords easier to remember, especially when they have to log in to many services. If just one other service suffers a credential breach, attackers can try the same username and password combination on the website’s administration page.
Another risk comes from online scams. Fake login pages can be designed to look almost identical to legitimate services, while the messages or emails leading to those pages often create a sense of urgency. If users enter their passwords into a fake form, attackers can use the information almost immediately. Automated guessing attempts also put pressure on accounts that use short or common passwords or lack a mechanism to limit the number of attempts.
MFA addresses part of the problem by requiring additional evidence of identity. An attacker may know the password but still have difficulty completing the login without the device or second authentication factor. However, its effectiveness depends on the method chosen, how it is configured, and the user’s ability to recognize unusual signs.
Common authentication methods
Authenticator apps are a common choice for administrator accounts. The app generates one-time codes based on time or on each individual request. The codes do not need to be sent over a mobile network, which can make them more convenient in some situations. During setup, users should store recovery information in a secure location and verify that they can log in before leaving the configuration screen.
Physical security keys provide a way to confirm identity directly with a specialized device. This method is useful for accounts with high-level privileges because users must possess the key and usually interact with it during login. The drawback is that organizations need a backup plan if the key is lost, damaged, or unavailable when needed.
Confirmation notifications on a device can make the process faster, but users should not accept every request simply because a notification appears. If an attacker repeatedly sends login requests, users may accidentally tap to approve one just to stop the annoying notifications. Therefore, they need to check the displayed information, reject requests they did not initiate, and report the issue to the responsible person if it happens repeatedly.
Codes sent by text message may be easier to deploy in some systems, but they should not automatically be considered the strongest method. Phone numbers can be exposed to risks such as lost devices, changes to subscriber information, or abuse through account-takeover schemes. When possible, businesses should prioritize a method appropriate to the account’s sensitivity and their actual operational capabilities.
Deploying MFA across different privilege levels
Not all accounts have the same level of impact. The highest-level administrator accounts, server access accounts, domain management accounts, and accounts authorized to change billing details should receive priority protection. MFA should then be extended to editors, support staff, and third-party accounts capable of modifying content or settings.
Before enabling MFA across the board, administrators should create a list of existing accounts, the owner of each account, and the corresponding scope of permissions. This list helps identify old accounts, shared accounts, or accounts that no longer have anyone responsible for them. An account with no clear owner not only makes recovery more difficult but also obscures accountability when an incident occurs.
Shared accounts are an issue that should be addressed early. When multiple people use the same login, it becomes difficult to determine who made a change, and managing authentication devices also becomes less transparent. A safer approach is to create individual accounts based on roles, grant only the permissions needed, and revoke access as soon as a person changes roles or stops working with the organization.
A recovery plan must be prepared before enabling MFA
MFA can cause disruption if users lose their devices, change phones, or delete their authenticator app without transferring its configuration. Therefore, a recovery plan must be developed in advance rather than waiting until an account is locked before trying to resolve the problem. Each important account should have at least one securely stored backup option, such as a second authentication device or recovery codes kept in a place accessible only to authorized personnel.
Recovery codes should not be stored in the same place as the password or left as a public note on a shared computer. Businesses need to define who may keep them, who may use them, and how the codes will be replaced after they have been used. If recovery codes are exposed, they must be disabled or reissued according to the system’s procedures.
The recovery support channel also needs to be protected. If support staff rely on only a few easily guessed pieces of information to verify identity, attackers may exploit this process itself to bypass MFA. Recovery should require multiple verification signals, fully record who approved it, and restore access only to the extent necessary.
MFA does not replace other security measures
MFA reduces the risk associated with exposed passwords, but it does not prevent every form of attack. Users can still be tricked into providing authentication codes on a real-time phishing page. A stolen login session can also create separate risks if the system lacks session-management, remote-logout, and abnormal-activity detection mechanisms.
Websites therefore still need to update their platforms, extensions, and server components according to an appropriate schedule. Access should be segregated, administrator accounts should not be used for everyday web browsing, and login and configuration-change logs should be monitored. Limiting failed login attempts, issuing alerts when an unusual location or device is detected, and periodically reviewing the account list all help form an additional layer of defense.
In addition, users need guidance on recognizing unusual authentication requests. An unexpected login notification, an email asking for an authentication code, or an offer to install emergency support software should all be verified through official channels. The habits of not sharing authentication codes, not approving unfamiliar requests, and reporting incidents early are no less valuable than installing a tool.
Checking effectiveness after deployment
Enabling MFA is only the first step. Administrators should periodically check whether all important accounts are protected, whether backup methods are still working, and whether accounts that are no longer used have been revoked. The review should also include open login sessions, previously trusted devices, and external applications that still have access.
A small-scale recovery exercise can reveal weaknesses that are not apparent in the settings. For example, a business may discover that the responsible person does not know where to obtain backup codes, that a second account has not been granted the necessary permissions, or that the approval process depends too heavily on one individual. Exercises should be conducted in a controlled manner, avoiding disruption to the website and not using real information in an unsafe way.
When an employee leaves or changes roles, access should be reviewed immediately rather than waiting for the next periodic check. Authentication devices, backup codes, and access to related tools must also be revoked or transferred according to policy. This step is often overlooked but is highly significant in preventing old accounts from continuing to exist outside organizational control.
Start with a plan suited to the website
An effective MFA plan does not have to be complicated from the outset. Website owners can begin by protecting the accounts with the highest privileges, eliminating shared accounts, preparing a recovery plan, and teaching users how to recognize fake authentication requests. Once the process is stable, protection can be expanded to other account groups.
The important thing is to choose a method that the organization can manage over the long term. A feature-rich solution without someone responsible for it, without a backup plan, or without regular testing will be unlikely to provide real-world security. Conversely, a clear process, separated privileges, and a recovery plan that is practiced regularly will help make MFA a sustainable part of website administration.
As administrator accounts become increasingly linked to multiple services, multi-factor authentication should be regarded as a basic standard rather than a measure used only after an incident has occurred. Combining MFA with unique passwords, regular updates, least-privilege access, log monitoring, and user training will create more layers of protection for the website and the data behind it.