

Managing Website Administrator Accounts: Reducing Access-Related Risks

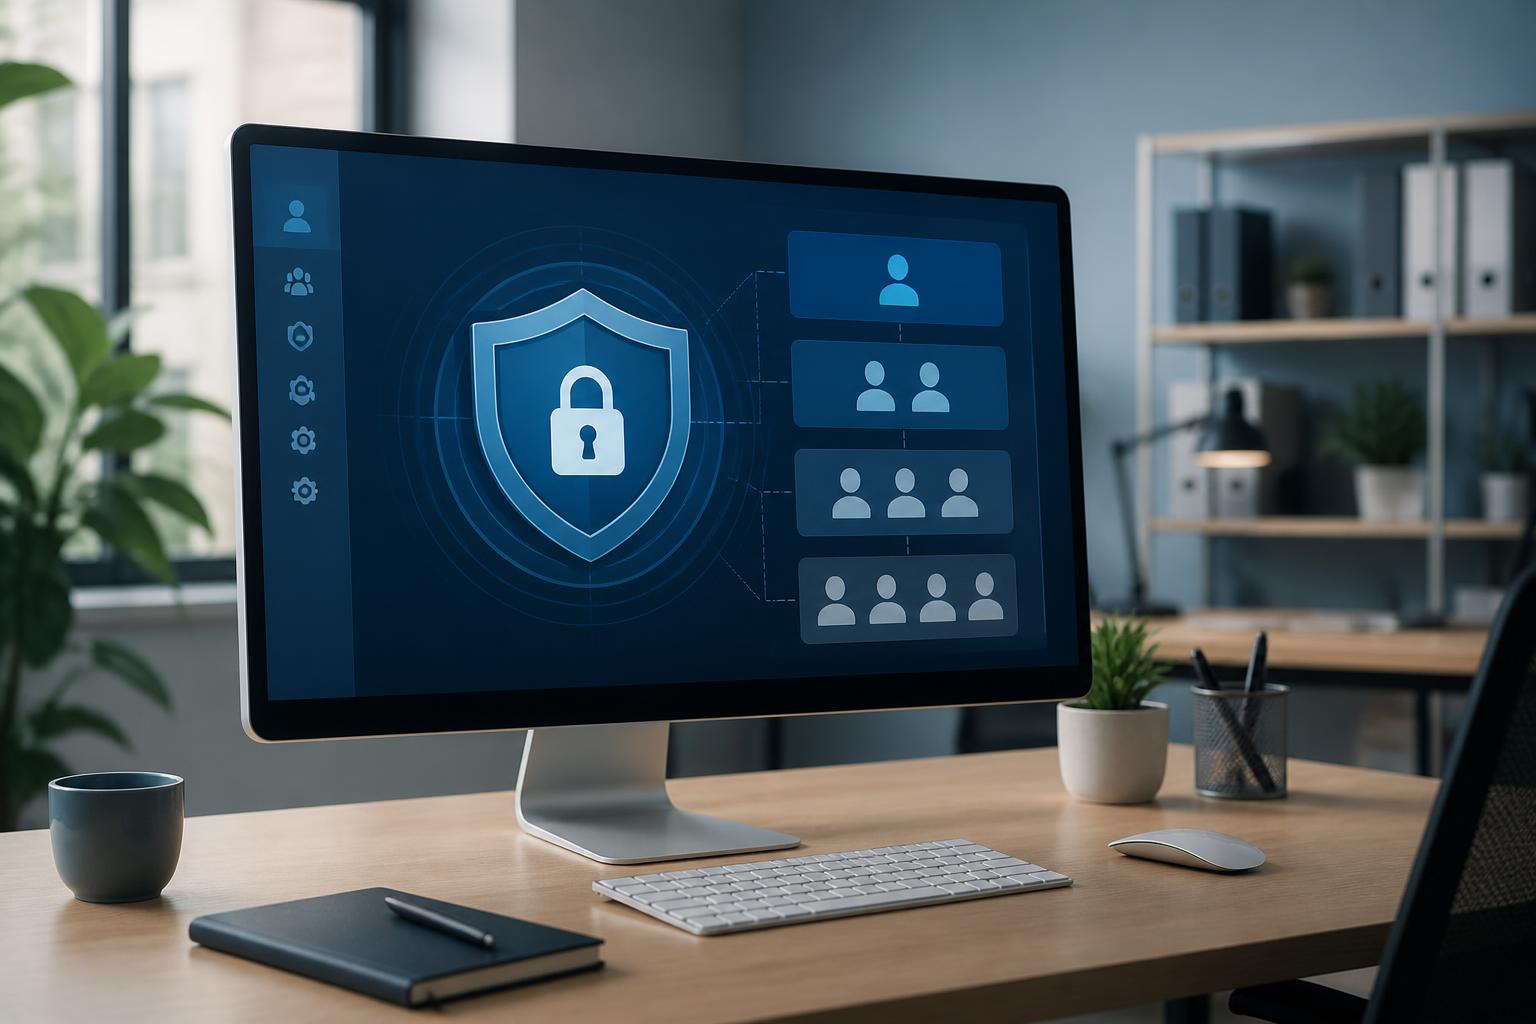
In many website protection plans, businesses often focus on servers, source code, SSL certificates, or anti-malware tools. However, another factor with an equally direct impact is how accounts with access to the website are managed. A shared account, a leaked password, or an employee who has left but still retains login access can all create a weakness that is difficult to detect within the system.
Managing administrator accounts is not simply a matter of setting a long password. It is a process that involves determining who is allowed access, which actions they are permitted to perform, how their identity is verified, and when their access must be revoked. When this process is designed properly, the website faces less risk of unauthorized modifications, data loss, or the installation of unwanted content.
Why does access need to be managed strictly?
Each administrator account is a door leading into part or all of the system. If everyone uses an account with the highest level of access, it will be difficult for the business to determine who made a change when an incident occurs. Investigation also becomes more complicated because activity logs record a shared username rather than a specific identity.
Shared accounts also increase the likelihood that passwords will be distributed through messages, email, or insecure storage tools. When a team member leaves the group, the password may have to be changed for everyone else. If this is delayed, someone who is no longer responsible may still be able to access the website.
Risks also arise when an employee or partner is granted more access than necessary. A person responsible for content may only need to create and edit articles, but if they are given permission to install plugins, change configurations, or manage users, an accidental action could affect the entire website. Properly assigning permissions helps limit the scope of impact if an account is exposed or misused.
The principle of least privilege
The most important principle is that each person should be granted only the permissions necessary to complete their work. A writer does not necessarily need permission to install new components. An employee responsible for advertising may need to view data or create campaign-related content, but should not automatically be allowed to change administrator users. A website development company may need technical access during a specific period, after which that access must be reviewed.
On content management systems, user roles are usually divided into multiple levels. The names and specific capabilities may vary by platform, but the general approach remains to separate system-wide administrative permissions from permissions for editing, publishing, or viewing data. Businesses should make a list of each position’s tasks before granting access, rather than choosing the highest-level role for convenience.
Permissions also need to be reviewed periodically. An account may once have needed special access to handle a short-term task, but that access may no longer be appropriate after the task is complete. Reviews help identify accounts that are no longer in use, accounts with unclear roles, or permissions that have expanded over time without a specific reason.
Each person should have an individual account
Individual accounts help the website record each member’s activity more accurately. When there is a clear history of changes, the manager can determine which content was edited, which account performed the action, and when the incident occurred. This provides a useful basis for both internal reviews and incident response.
Creating individual accounts does not mean giving everyone the highest level of administrative access. On the contrary, individual accounts need to be paired with appropriate roles. A team can use separate accounts for editing, design, technical work, and management instead of sharing a single set of login credentials.
For accounts belonging to vendors or external partners, access should have a defined duration and purpose. Once the work is complete, the business should disable or delete those accounts. If a partner needs periodic support access, it should still be activated as needed rather than left open continuously without anyone being responsible for monitoring it.
Strong passwords and multi-factor authentication
Passwords for administrator accounts need to be sufficiently long, difficult to guess, and not reused across multiple services. Easily associated information such as the brand name, domain name, founding date, or phone number should not be a primary component of a password. Each important account should have its own password so that exposure of information from one service does not create risks for other services.
Businesses can use an appropriate password manager to create and store login information. This reduces the need to write passwords on paper, keep them in unprotected files, or share them in group conversations. Access to the password vault should also be restricted, and there must be a process for changing access when the responsible member is no longer working with the organization.
If the platform supports multi-factor authentication, this feature should be enabled for accounts with administrative privileges. Login will then rely not only on a password but also on an additional verification method. Multi-factor authentication does not replace strong passwords and proper permission assignment, but it adds another layer of protection if a password is exposed.
Information used to recover an account also needs to be managed carefully. The recovery email address must remain active, be protected, and belong to the correct person or responsible department. The business should know who can receive recovery codes, where backup codes are stored, and how to handle the situation when the person responsible changes.
Processes for granting, changing, and revoking access
A simple process can begin with a clearly documented access request. The request should state the user, the task, the scope of access, and the required period of use. An authorized person should approve it before the account is created or its privileges are elevated. This approach helps prevent access from being granted out of habit or through verbal requests that are difficult to review later.
When a team member changes positions, their access should be reviewed rather than left unchanged by default. When an employee leaves, the related accounts should be locked or revoked within a timeframe appropriate to the internal process. In addition to website administrator accounts, the business should also check access to servers, domains, email services, analytics tools, and related platforms.
For emergency accounts, the business can establish separate procedures for storage and use, but should not turn such an account into one used daily by everyone. Information about the emergency account must be protected, its use must be recorded, and the password should be changed after necessary uses.
Reviewing logs and identifying unusual signs
Activity logs can provide information about logins, content changes, component installations, or user-permission updates, depending on the platform’s capabilities. Administrators should know where the system stores logs, how long the data is retained, and who has permission to view it. Not every change is a sign of an attack, but activity outside working hours or activity that does not match an account’s responsibilities should be verified.
Some signs that deserve attention include the appearance of a new account with no clear creator, a change to the administrator email address, content being edited outside the plan, unfamiliar plugins or components being installed, or multiple consecutive failed login attempts. When an anomaly is detected, the business should not simply delete the altered content and ignore the cause. It needs to identify the account involved, check permissions, change authentication information, and assess whether the incident affected any other data.
Keeping review information also helps the business learn from experience. If an account was mistakenly granted excessive permissions, the approval process may need to be adjusted. If multiple people still have to use a shared account because the platform has not been configured properly, this is a sign that the organization of work and the administrative tools need to be improved.
Balancing security and work efficiency
Access controls should not force employees to find ways around the process because it is too complicated. Businesses need to create concise guidelines, clearly identify approvers, and provide support options when there is a legitimate need. Permissions should be sufficient to complete the task, but every expansion of access must have a reason and an expiration period.
Training also plays an important role. Website users need to know how to recognize suspicious login requests, avoid sending passwords through inappropriate channels, and report immediately when they lose an authentication device or detect unusual activity. A good process will be difficult to apply effectively if users do not understand why these steps are necessary.
Managing administrator accounts is an ongoing task, not something performed only once when a website is handed over. As the team, partners, platform, and business objectives change, the list of users and their access permissions must also be updated. Periodic reviews, the use of individual accounts, least-privilege access, password protection, and enabling multi-factor authentication are practical steps that can be implemented in stages.
A safer website depends not only on technology but also on how people use that technology. When access is granted to the right person, within the right scope, and at the right time, the business can reduce many unnecessary risks while creating a clearer foundation for operations, collaboration, and incident response.